

Prerequisites
- A Concord account that belongs to at least one workspace.
- The browser your client opens must be able to sign in to app.concord.ad. Authorization never signs anyone in by itself.
Client setup
- Claude Code
- Claude Desktop and claude.ai
- Other clients
/mcp in the session if it does not). The tools then appear as mcp__concord__askConcord, mcp__concord__prepareUpload, and mcp__concord__attachUpload.2026-07-28 and the previous handshake-based revision 2025-11-25, which every released client negotiates today.
How authorization works
Concord is both the OAuth 2.1 authorization server and the MCP resource server, so the whole flow runs againstapi.concord.ad. Clients discover it on their own; you only see the approval screen.
1
The client calls the endpoint
The first unauthenticated request is answered with a
401 and a WWW-Authenticate challenge pointing at /.well-known/oauth-protected-resource/mcp.2
Discovery and registration
The client reads the protected-resource and authorization-server metadata, then registers itself at
/auth/oauth2/register (Dynamic Client Registration). Registration is open and needs no credentials. It is rate limited per IP address; a client over the limit gets 429.3
You approve the connection
The browser opens Concord’s approval screen, described below.
4
The client receives a token
Standard authorization-code flow with PKCE. Concord asks for
openid and offline_access: the token identifies you, your Concord permissions decide the rest, and offline_access earns a refresh token so the connection stays alive without the browser.The approval screen
You must be signed in to Concord in that browser. The screen shows:- Verified app or Unverified app. Concord verifies Claude and ChatGPT by their registered callback addresses. Any other client is unverified: its name was chosen by whoever registered it.
- The question “Allow” followed by the app name, and what the app will be able to do: talk to the Concord agent on your behalf, read your campaigns and their performance, and upload files. Changes on your platforms still go through your approval in Concord.
- Where you will be sent once you allow it.
- The workspace: a choice of workspaces if you belong to several, or the one workspace it will reach.
- For an unverified app, a checkbox confirming you started the connection yourself, required before Allow is enabled.
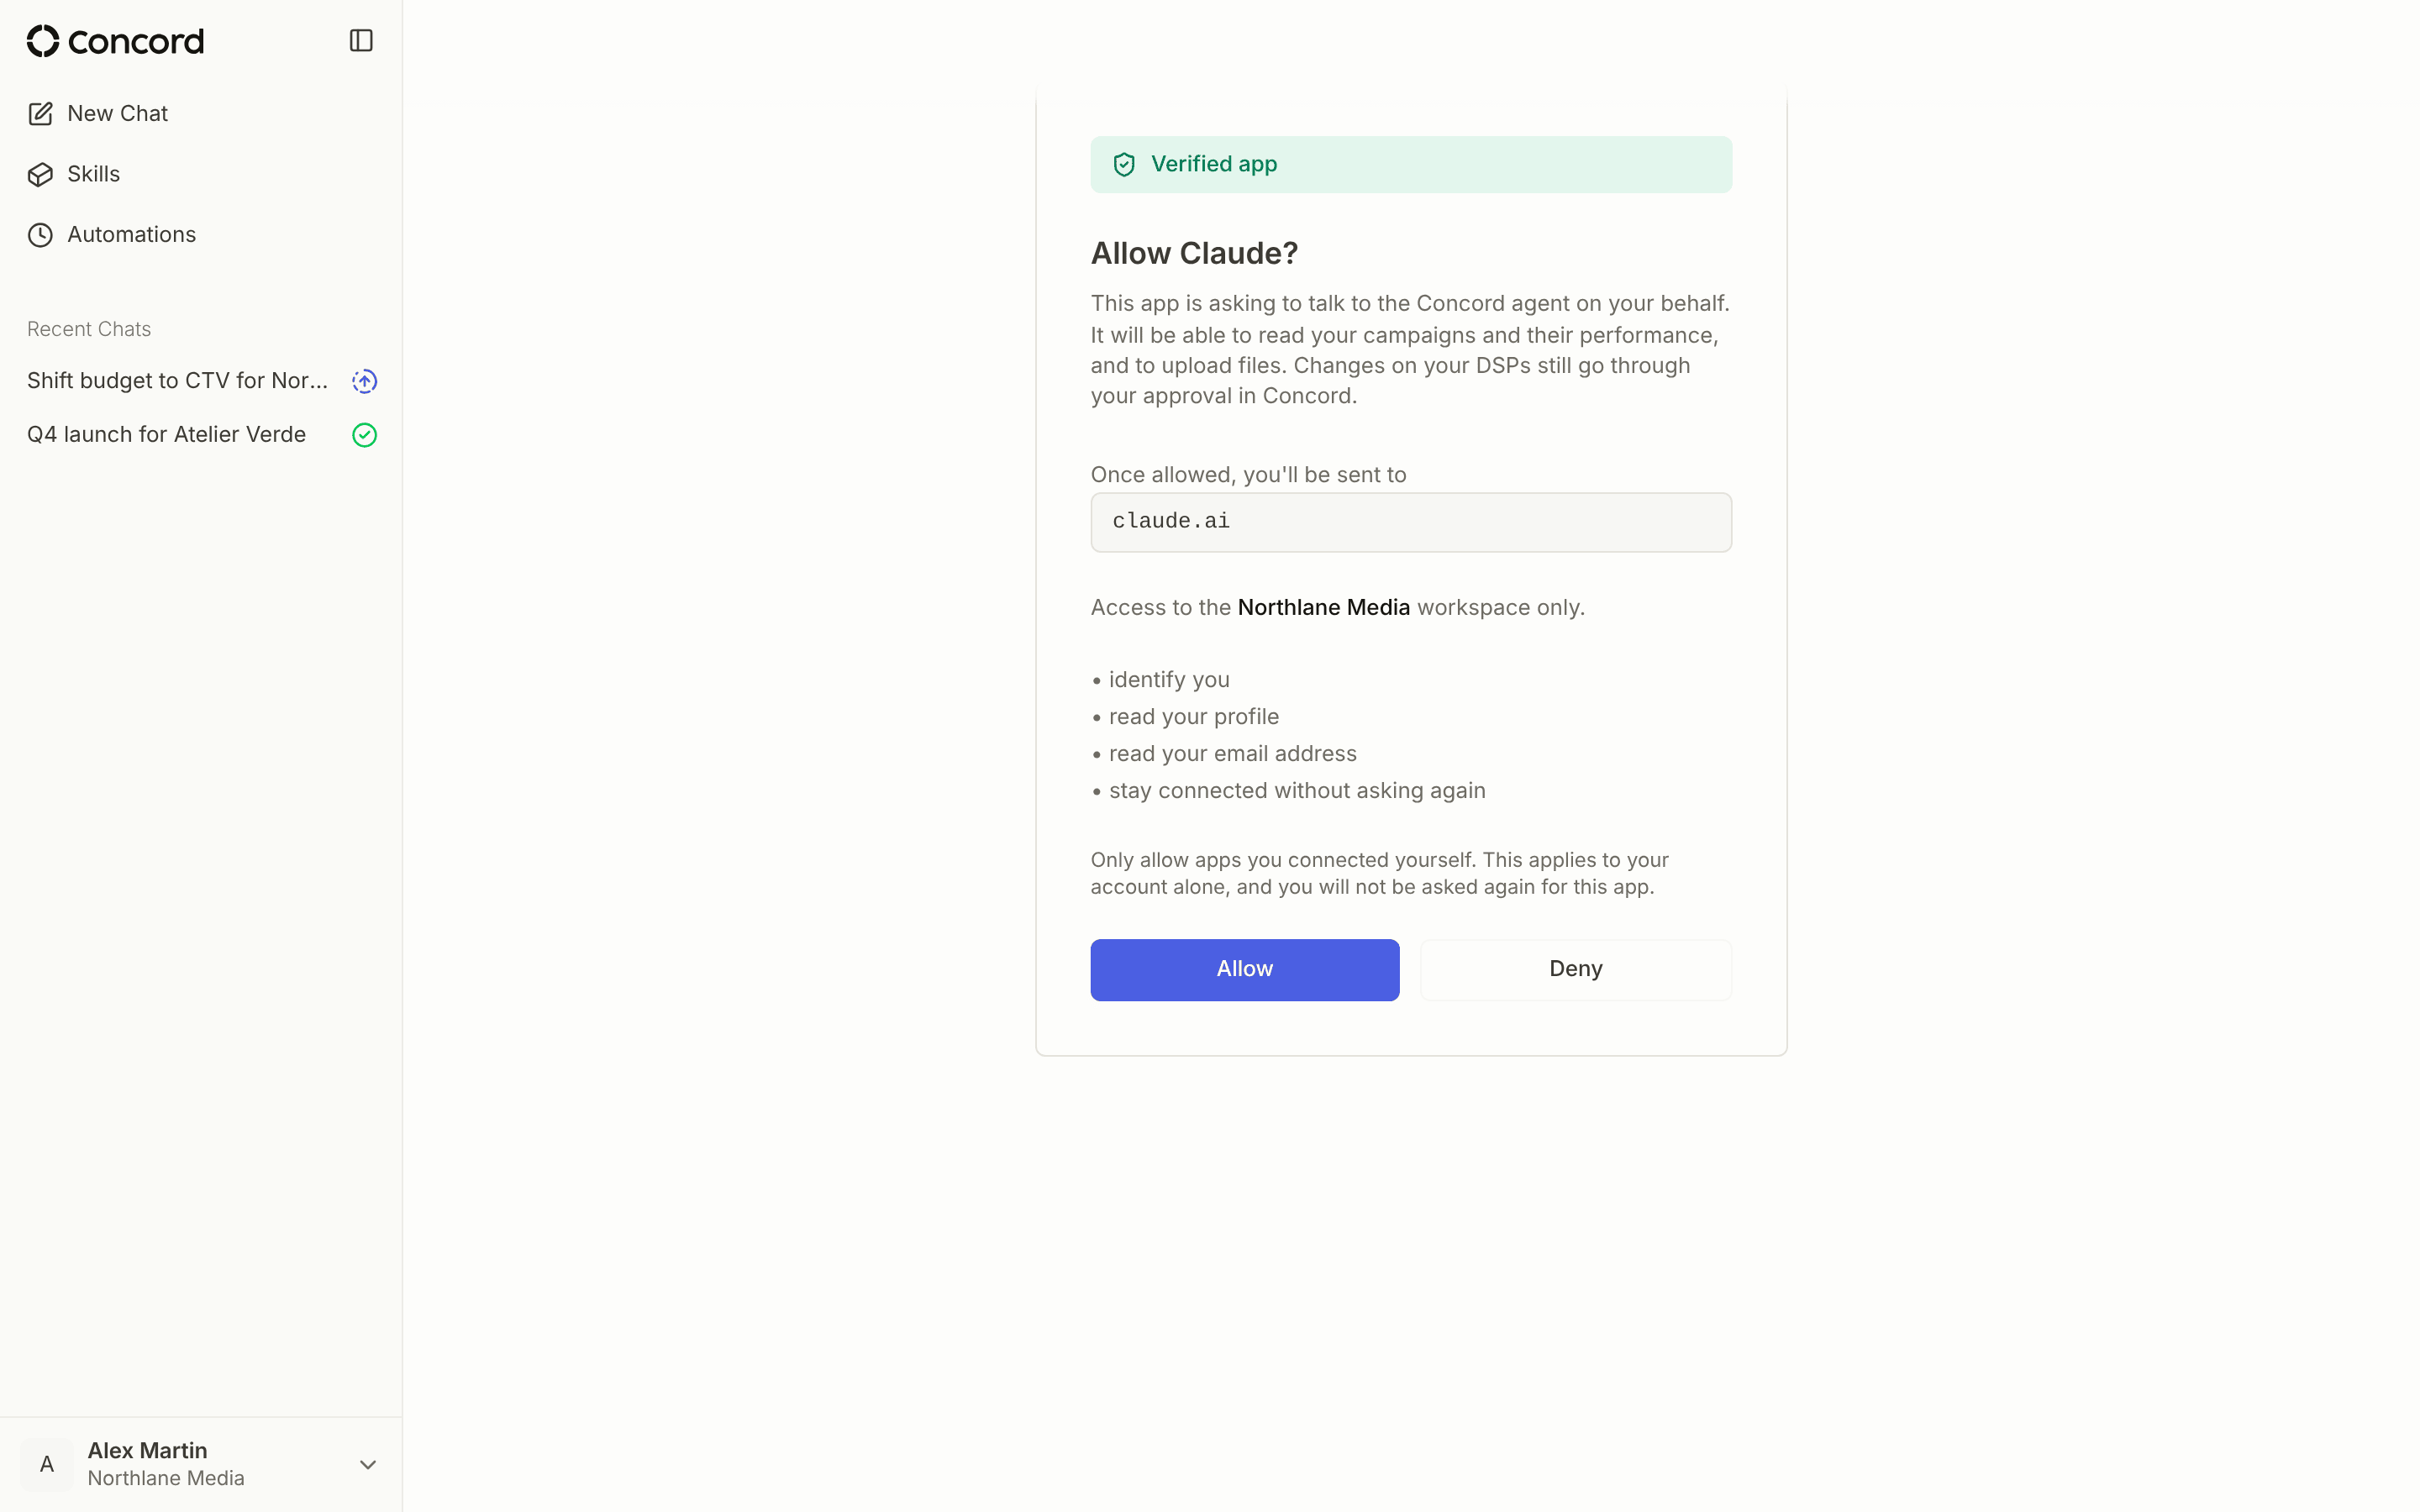
access_denied to the client.