

Open Connectors
Open the Salesforce card in Settings → Connectors.
- Create and configure an External Client App in Salesforce
- Enter its Consumer Key and Secret on the Salesforce card in Concord
- Authorize the connection
You need Salesforce permissions to manage External Client Apps in your org, and the org must have access to Salesforce hosted MCP servers. Salesforce’s own guide, Create an External Client App for MCP, covers the Salesforce side in detail.
1. Create an External Client App in Salesforce
1
Open External Client App Manager
In Salesforce, open Setup and search for External Client App Manager, or go to Apps → External Client Apps → External Client App Manager.You can also open it directly, replacing the domain with your org’s My Domain:
2
Create the app
Click New External Client App and name it
Concord.3
Set the callback URL
Enable OAuth for the app and use exactly this callback URL. The Salesforce card in Concord shows it too, with a copy button.
4
Add the OAuth scopes
Add both of these scopes:
- Perform requests at any time (
refresh_token, offline_access) - Access Salesforce hosted MCP servers (
mcp_api)
5
Enable the flow and PKCE
Under Flow Enablement, enable Authorization Code and Credentials Flow. Under Security, make sure Require Proof Key for Code Exchange (PKCE) extension for Supported Authorization Flows is enabled. Save the app.
6
Get the Consumer Key and Secret
Open the Concord External Client App and go to Settings → OAuth Settings → Consumer Key and Secret. Copy the Consumer Key and the Consumer Secret.
2. Enter the credentials in Concord
1
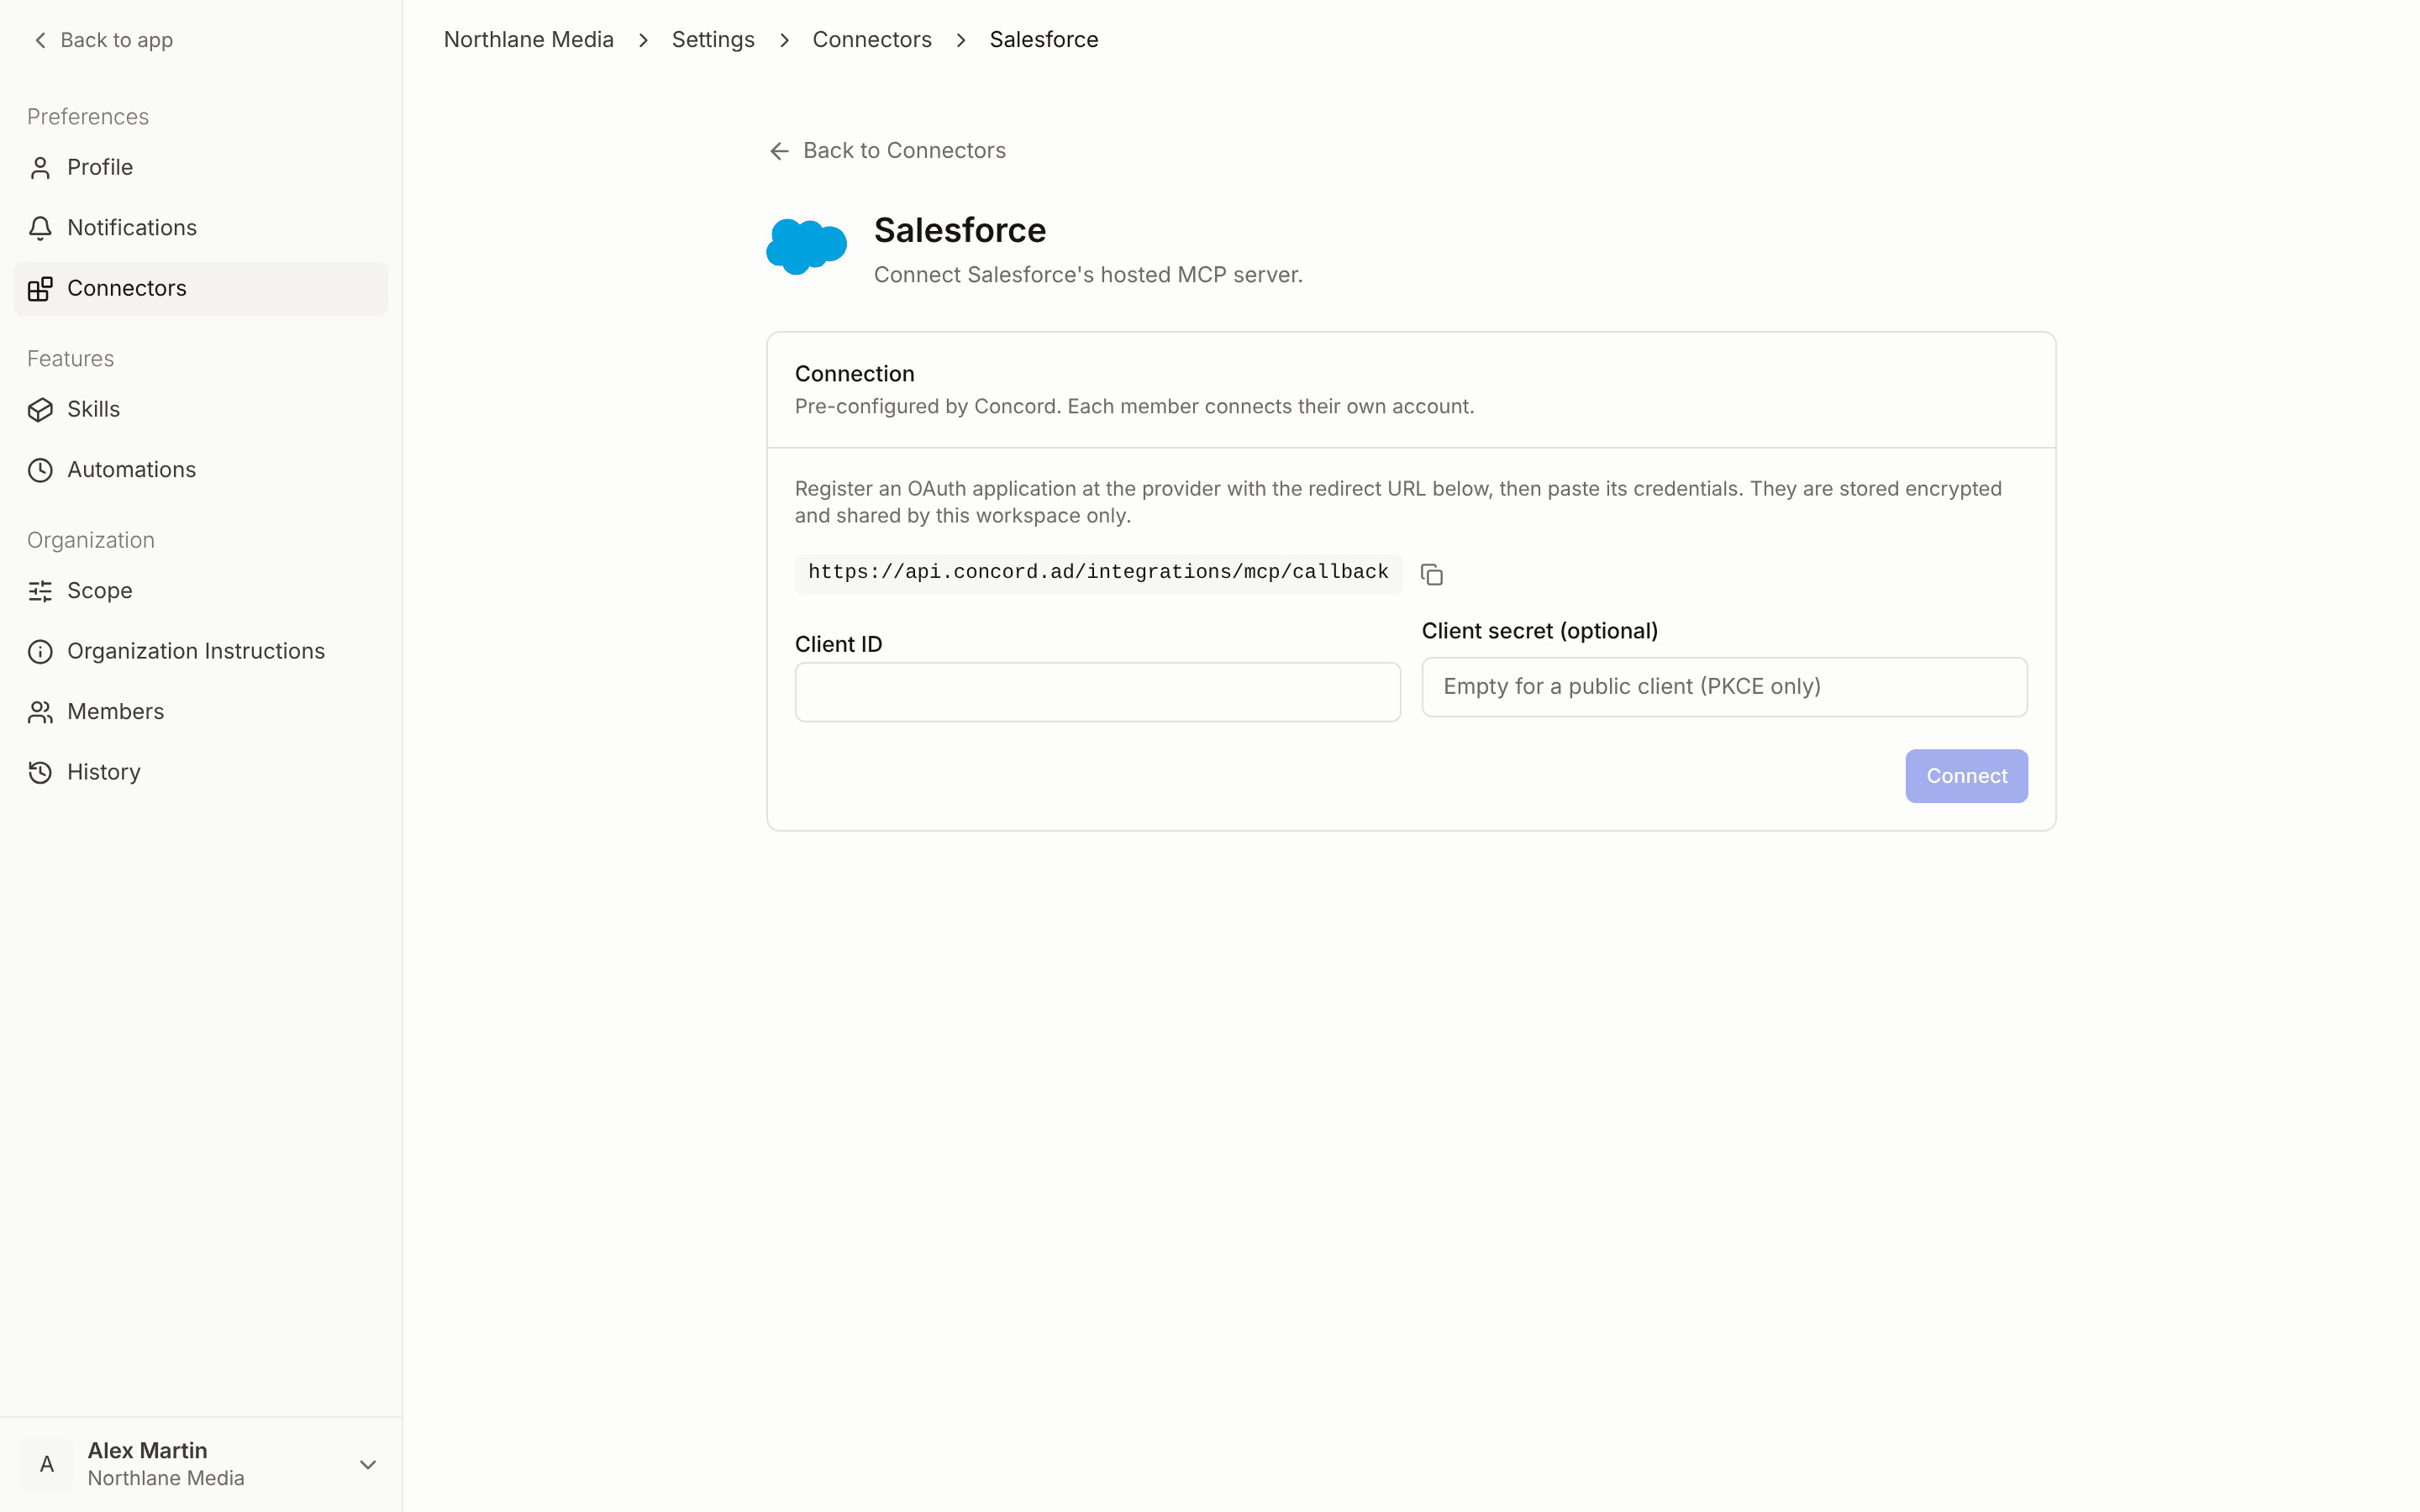
Open the Salesforce card
In Concord, go to Settings → Connectors and open Salesforce.
2
Fill in the form
The page asks for your workspace’s OAuth application:
The credentials are stored encrypted and used by your workspace only.
3
Connect
Click Connect. Concord sends you straight to Salesforce.
3. Authorize in Salesforce
Sign in to Salesforce if prompted, then authorize the Concord application. You come back to the Salesforce connector page in Concord, which shows Connected. Its tools are now available in your conversations.For the rest of your team
The OAuth client is entered once per workspace. Every other member opens the Salesforce card and clicks Connect my account to sign in with their own Salesforce user. Concord then sees in Salesforce what that member can see.Managing the connection
On the Salesforce connector page:- Test connection checks the connection and lists the tools Concord can use.
- Disconnect my account removes your connection; Reconnect signs in again.
- Replace OAuth client lets you enter a new Consumer Key and Secret, for example after rotating them in Salesforce.
- Share my connection with the workspace lets members who have not connected their own account use yours. Concord then acts as you for them. Off by default.
- Available in this workspace hides the connector from Concord for everyone while keeping it configured.
- Remove from workspace removes the connector and every member’s connection.
Configuration reference
Useful links
- Create an External Client App for MCP: Salesforce’s official guide
- External Client App Manager in your org:
https://YOUR_SALESFORCE_DOMAIN/lightning/setup/ManageExternalClientApplication/home